Enterprise AI Agents: How Companies Run AI Agents at Scale
Enterprises do not fail at AI agents because the technology is immature. They fail because a pilot that impressed five executives was never designed to survive fifty departments, three compliance reviews, and an identity system from 2012. The 88% that die are killed by architecture, not ambition.
Quick answer: Enterprises run AI agents at scale by treating every agent as privileged software: a scoped identity per agent, least-privilege access to systems, audit logs of every action, human approval on high-stakes decisions, and a named business owner accountable for behavior. The agents themselves are simple; the governance around them is the engineering.
Key takeaway: Enterprise scale multiplies everything — agents, credentials, failure modes, and auditors. IDC data shows 88% of pilots never reach production, and the surviving pattern is consistent: start with one workflow per department, run agents through existing change-management processes, centralize credentials, and measure ROI per agent like any employee's output. Scale is a governance product, not a model upgrade.
TL;DR:
- Agents are privileged software: scoped identities, least-privilege access, audit trails — not chat toys with admin keys.
- Every agent gets an owner: a business person accountable for behavior, not just a developer who deployed it.
- Central governance beats scattered configs: one credential vault, one approval framework, one exception-review ritual.
- The numbers decide survival: 88% of pilots fail on integration and governance; measured baselines are the difference.
Table of Contents
What Are Enterprise AI Agents?
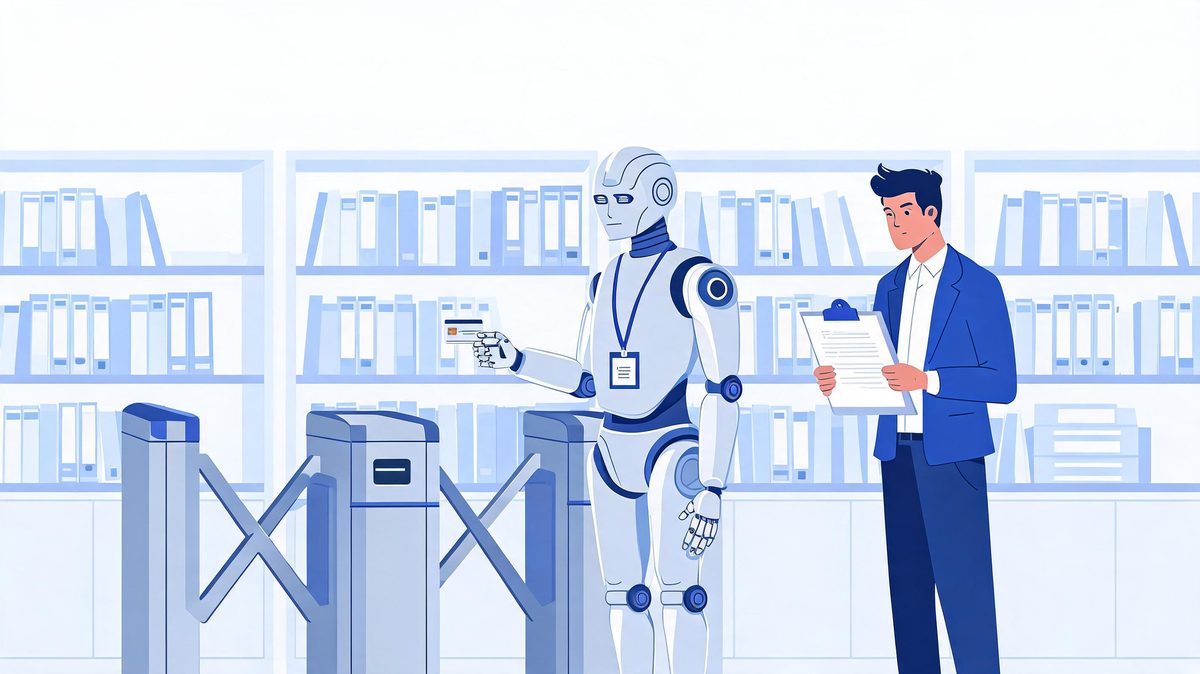
Enterprise AI agents are AI agents deployed across a large organization with formal governance: scoped identities, permission controls, audit logging, monitoring, and a named owner accountable for every action. The definition differs from a startup pilot in one word — governance — and that word costs most of the budget.
What are enterprise AI agents?
What are enterprise AI agents? Enterprise AI agents are AI agents deployed across a large organization under formal governance: each agent holds a scoped identity, accesses only required systems, logs every action to an audit trail, and answers to a named business owner.
According to IDC research, 88% of AI agent pilots never reach production, and the blockers are integration architecture, data readiness, security review, and unclear ownership rather than model quality (Sources: IDC, 2026). Gartner forecasts $2.595 trillion in AI spending for 2026, and 28% of organizations are rewiring workflows for agents (Sources: Gartner, McKinsey, 2026).
For example, an enterprise support agent using Microsoft Entra inherits the company identity system, carries documented write scopes, and reports decisions to a compliance dashboard. We found the governance investment pays twice: once in security approval and once in earned autonomy.
First, treat agents as privileged software from day one. Second, budget governance as core engineering. Finally, let the audit log argue for autonomy.
The Architecture: Identity, Access, and Governance
Enterprise agent architecture has four layers, and the model sits at the bottom of the stack — below identity, below access control, below audit. That ordering surprises people; it should not.
How do enterprises govern multiple AI agents?
How do enterprises govern multiple AI agents? Enterprise governance of multiple AI agents is the central control layer with five functions: scoped identity per agent, least-privilege access, central credential management, complete audit logging, and change management for agent updates.
According to enterprise deployment analyses from Grid Dynamics and IDC, data readiness and unclear ownership join identity as the top scaling blockers, and 88% of pilots never reach production for these reasons (Sources: Grid Dynamics, IDC, 2026). Gartner counts 40% of agentic projects canceled, and only 23% of organizations have reached broader deployment (Sources: Gartner, Zscaler, 2026).
For example, an enterprise using Microsoft Entra runs twenty departmental agents and answers questions a pilot never faced: which agent holds which credentials, who approves new access, and how conflicts resolve. We found mature deployments assign every agent a business owner and a technical owner.
First, give each agent a scoped badge in the identity provider. Second, route credentials through a central vault. Finally, review agent behavior where releases are approved.
| Layer | Function | Enterprise Control |
|---|---|---|
| Identity | Each agent has a distinct identity | SSO/Entra integration, per-agent credentials |
| Access | Least-privilege system access | Field-level scopes, no shared keys |
| Audit | Every action recorded | Immutable logs, retention policy |
| Change mgmt | Updates reviewed and rolled out | Staging, rollback, release notes |
| Ownership | Accountable business owner | Named owner per agent |
Running Multiple Agents Without Chaos
One agent is a workflow. Twenty agents are an operating model. The questions that never came up in the pilot define enterprise reality.
How do multiple AI agents work together in an enterprise?
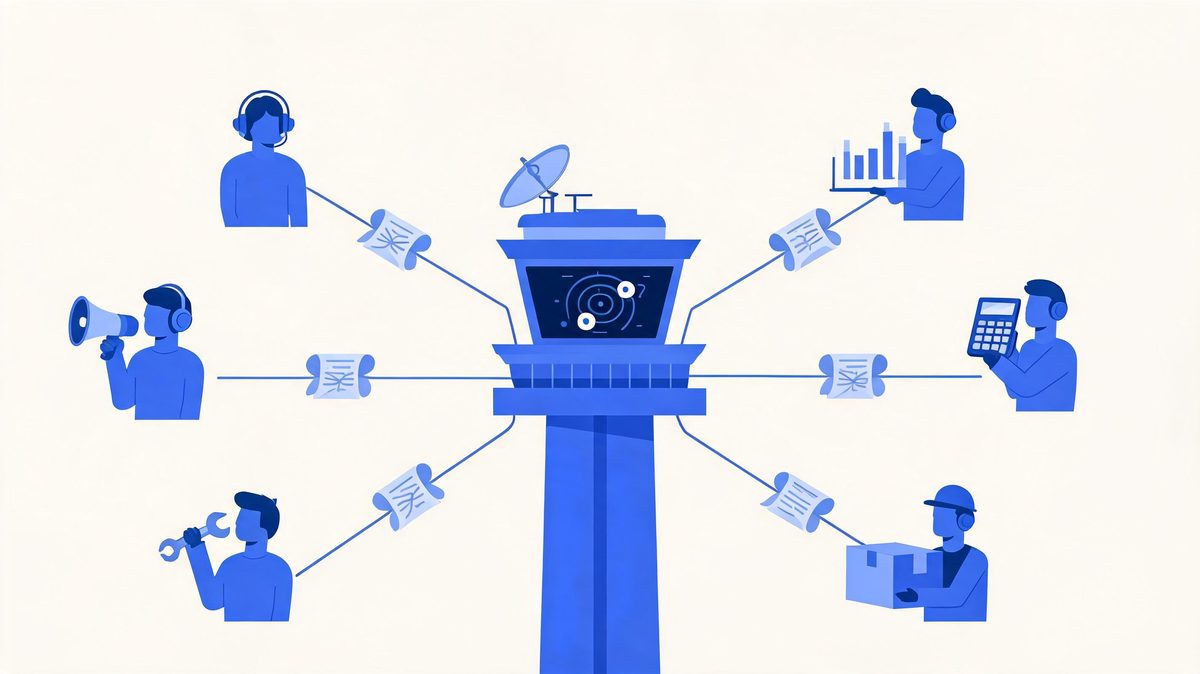
How do multiple AI agents work together in an enterprise? Multi-agent orchestration is the enterprise pattern where a control layer assigns tasks, resolves conflicts, and enforces boundaries between agents.
According to enterprise architecture analyses from Grid Dynamics and Appian, multi-agent patterns range from a central orchestrator delegating work to peer agents communicating through protocols like MCP (Sources: Grid Dynamics, Appian, 2026). The stakes scale fast: 62% of organizations now run agent experiments, IDC finds 88% of naive deployments stalling on coordination, and Gartner forecasts $2.595 trillion in AI spending for 2026 (Sources: Zscaler, IDC, Gartner, 2026).
For example, a refund touches a support agent validating the request, a finance agent checking policy limits, and an operations agent processing the transaction, each scoped to a separate system, logging to one audit trail. We found every inter-agent handoff deserves API-contract scrutiny.
First, map which agents touch which systems before adding a new agent. Second, define conflict rules for overlapping territory. Finally, review handoff logs monthly.
Measuring Enterprise Agent ROI
What is the ROI of enterprise AI agents?
What is the ROI of enterprise AI agents? Enterprise agent ROI is the measured return across three baselines per agent: hours saved per workflow against the manual process, error reduction comparing defects caught versus introduced, and cost avoided through downstream failures prevented by verification steps.
According to Gartner, over 40% of agentic AI projects are canceled for unclear value and high risk (Sources: Gartner, 2026), and MIT-affiliated researchers found 95% of generative AI pilots delivered no measurable ROI (Sources: MIT via Tricentis, 2026). For example, an enterprise support agent earning its keep shows a deflection rate, a customer-satisfaction delta, and hours returned to the team, three numbers a CFO reads.
We found the ROI case lives or dies on the baseline: enterprises that measured manual performance before deployment report gains, and those that did not report opinions.
First, instrument the manual process before automating anything. Second, publish the numbers per agent and per department. Finally, retire underperforming agents, because killing failures funds the survivors.
The Enterprise Deployment Checklist
Print this list. Walk it before every agent goes live. The enterprises shipping at scale run the same ten checks, every time:
Enterprise Agent Go-Live Checklist
- Named business owner — accountable for the agent's behavior, not just its uptime
- Scoped identity — per-agent credentials in the central vault, least-privilege access
- Documented workflow — plain-language steps, exception paths, and approval thresholds
- Measured baseline — pre-launch hours, errors, and turnaround, on record
- Audit trail — every action reconstructible, retention policy set
- Kill switch — tested, with a defined pull-trigger
- Security review — permission matrix signed off by security, not just IT
- Rollback plan — documented and rehearsed
- ROI dashboard — per-agent numbers visible to the owner weekly
- Retirement criteria — the conditions under which the agent gets turned off
McKinsey's March 2026 survey found only 28% of organizations pursuing fundamental workflow rewiring (Sources: McKinsey, 2026) — and that minority is where the production agents live. The checklist is long because scale is unforgiving, but every item is a one-time setup cost that pays for itself with each additional agent.
FAQs
What are enterprise AI agents?
AI agents deployed across a large organization with formal governance: scoped identities, permission controls, audit logging, monitoring, and a named business owner. They differ from pilot agents by operating inside compliance, security, and change-management processes.
How do enterprises govern multiple AI agents?
Through a central control layer: per-agent scoped identities, centralized credential vaults, least-privilege access, complete audit logs, and change management that treats agent updates like software releases. Every agent has both a business and a technical owner.
What is the ROI of enterprise AI agents?
Measured per agent against three baselines: hours saved per workflow, error reduction, and throughput gains, compared against platform, integration, and governance costs. Gartner counts over 40% of agentic projects canceled for unclear value — instrumented baselines are what keep programs funded.
How many AI agents does an enterprise need?
No fixed number. Mature enterprises commonly run tens of agents across support, sales, finance, operations, and IT. The count follows the workflows: every agent must justify its existence with a measured baseline and an owner, or it becomes a liability.
What is the biggest blocker for enterprise AI agents?
Integration architecture, data readiness, security review, and unclear ownership — IDC attributes 88% of pilot failures to these rather than model quality. At enterprise scale, identity management and governance become the largest engineering work.
Should enterprises build on vendor-native or custom platforms?
Vendor-native platforms like Salesforce Agentforce and Microsoft Copilot Studio inherit identity, compliance, and audit infrastructure, making them the faster path for most enterprises. Custom frameworks suit unique workflows or strict data-residency needs. The choice follows the existing stack and compliance requirements.
The Bottom Line
Enterprise AI agents reward the same discipline every other production system demands: scoped identities, least-privilege access, audit trails, named owners, measured baselines, and the willingness to retire what underperforms. IDC's 88% failure rate is not a verdict on the technology — it is a map of where the bodies are buried, and every marked spot is a governance gap. The path runs from one workflow with a measured baseline, through staged autonomy earned by audit logs, to a portfolio of agents managed like any other privileged software estate. The AI agent integration pillar guide holds the foundation, the workflow automation guide covers the monitoring ritual, the platform comparison frames the stack decision, and the business use-case guide makes the ROI case. Scale is not a bigger pilot. Scale is governance, repeated.
Sources
- IDC — 88% of AI agent pilots never reach production, via Institute PM and Innoflexion, 2026
- Gartner — 40%+ agentic AI project cancellations; $2.595T AI spending forecast, 2026
- MIT-affiliated research via Tricentis — 95% of generative AI pilots delivered no measurable ROI, 2026
- McKinsey March 2026 survey — 28% pursuing fundamental workflow rewiring
- Zscaler Digital Experience Predictions 2026 — agent deployment stages
- Grid Dynamics, Appian — enterprise multi-agent architecture and MCP patterns, 2026